Cyber threats have evolved dramatically over the last few years. Today's attackers are using increasingly sophisticated techniques that can bypass traditional antivirus software, making it harder for businesses to protect their systems, data and people.
Many legacy security tools rely on recognising known threats. While this approach can still identify some attacks, modern cybercriminals are constantly developing new methods designed to evade signature-based detection. As a result, organisations need a more intelligent approach to endpoint security.
This is where Endpoint Detection and Response (EDR) comes in.
EDR provides continuous monitoring of laptops, desktops, servers and other connected devices, enabling organisations to identify suspicious behaviour and respond to threats before they can cause significant damage. Rather than simply looking for known malicious files, EDR solutions analyse how applications and users behave, helping to identify threats that would otherwise go unnoticed.
To understand the difference EDR can make, imagine an employee receives what appears to be a legitimate invoice from a trusted supplier. Without realising it's malicious, they open the attachment and unknowingly trigger ransomware. In a traditional environment, the malware could begin encrypting files, spreading across the network and disrupting business operations before anyone notices.
With a modern EDR solution, that suspicious activity is identified almost instantly. The platform recognises unusual behaviour, automatically stops the malicious process, isolates the affected device and prevents the attack from spreading further. Security teams are alerted in real time, while detailed forensic information reveals exactly what happened and where the threat originated. What could have become a major business disruption is contained before it has the opportunity to escalate.
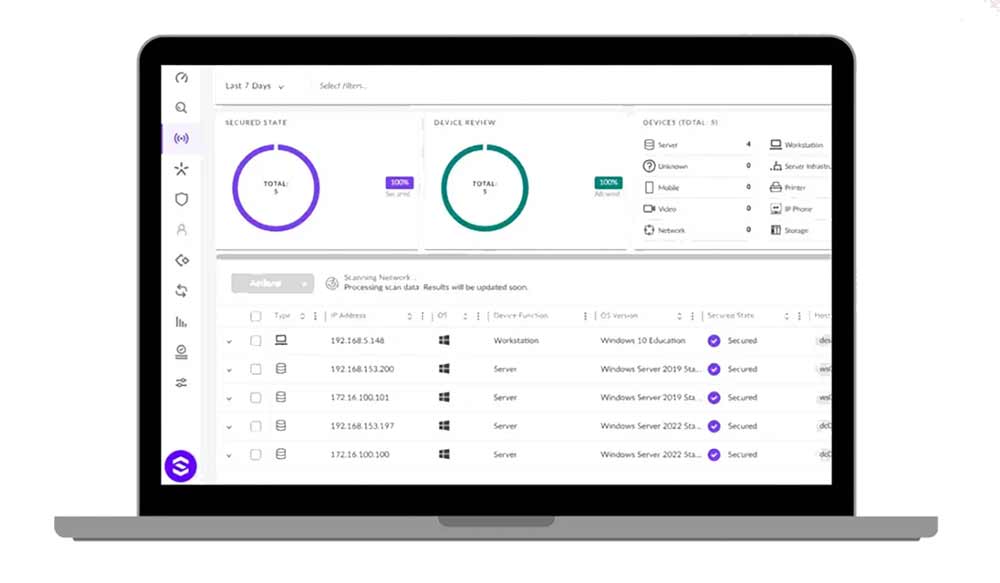
At Simoda, we work with organisations across a range of sectors to strengthen their cybersecurity posture using SentinelOne, a leading EDR platform that combines artificial intelligence, automation and real-time threat detection.
One of the key advantages of SentinelOne is its ability to identify threats based on behaviour rather than relying solely on prior knowledge of attacks. This means it can detect emerging threats, fileless malware and sophisticated cyberattacks that traditional antivirus products may miss.
The power of artificial intelligence also helps security teams gain greater visibility into potential threats. Rather than dealing with countless alerts and logs, SentinelOne automatically connects related events to create a clear picture of how an incident occurred. This enables faster investigations and helps organisations understand the full scope of a security event without overwhelming internal teams.
The longer a threat remains active within an environment, the more damage it can potentially cause. SentinelOne is designed to respond automatically when malicious activity is detected, stopping harmful processes, isolating compromised devices and preventing attacks from spreading. In the event of ransomware, the platform can even help restore systems to a pre-attack state, minimising disruption and reducing recovery time.
As businesses continue to embrace hybrid working and distributed workforces, maintaining visibility across every endpoint has become increasingly important. Employees are accessing systems from multiple locations and devices, creating new opportunities for attackers. SentinelOne's lightweight agent provides consistent protection across Windows, macOS and Linux devices, ensuring organisations can maintain security regardless of where users are working.
Simoda takes a consultative approach to cybersecurity. We work closely with businesses to understand their specific risks, operational requirements and long-term objectives. Whether an organisation has an in-house IT team that requires additional cybersecurity expertise or needs a trusted technology partner to act as its complete IT department, we can provide the support and protection required. From initial deployment through to ongoing optimisation, we help businesses maximise the value of their security investments while building a stronger and more resilient security posture.
Cyber threats aren't slowing down, and neither should your approach to protecting your business. By combining advanced EDR technology with expert guidance and support, organisations can move beyond traditional antivirus and take a more proactive approach to cybersecurity.
If you'd like to strengthen your cyber defences and better protect your business from modern threats, speak to the team at Simoda to learn how SentinelOne and our managed cybersecurity services can help.
simoda.co.uk


